Your Office Policy Changed. Your Security Policy Needs To Catch Up.
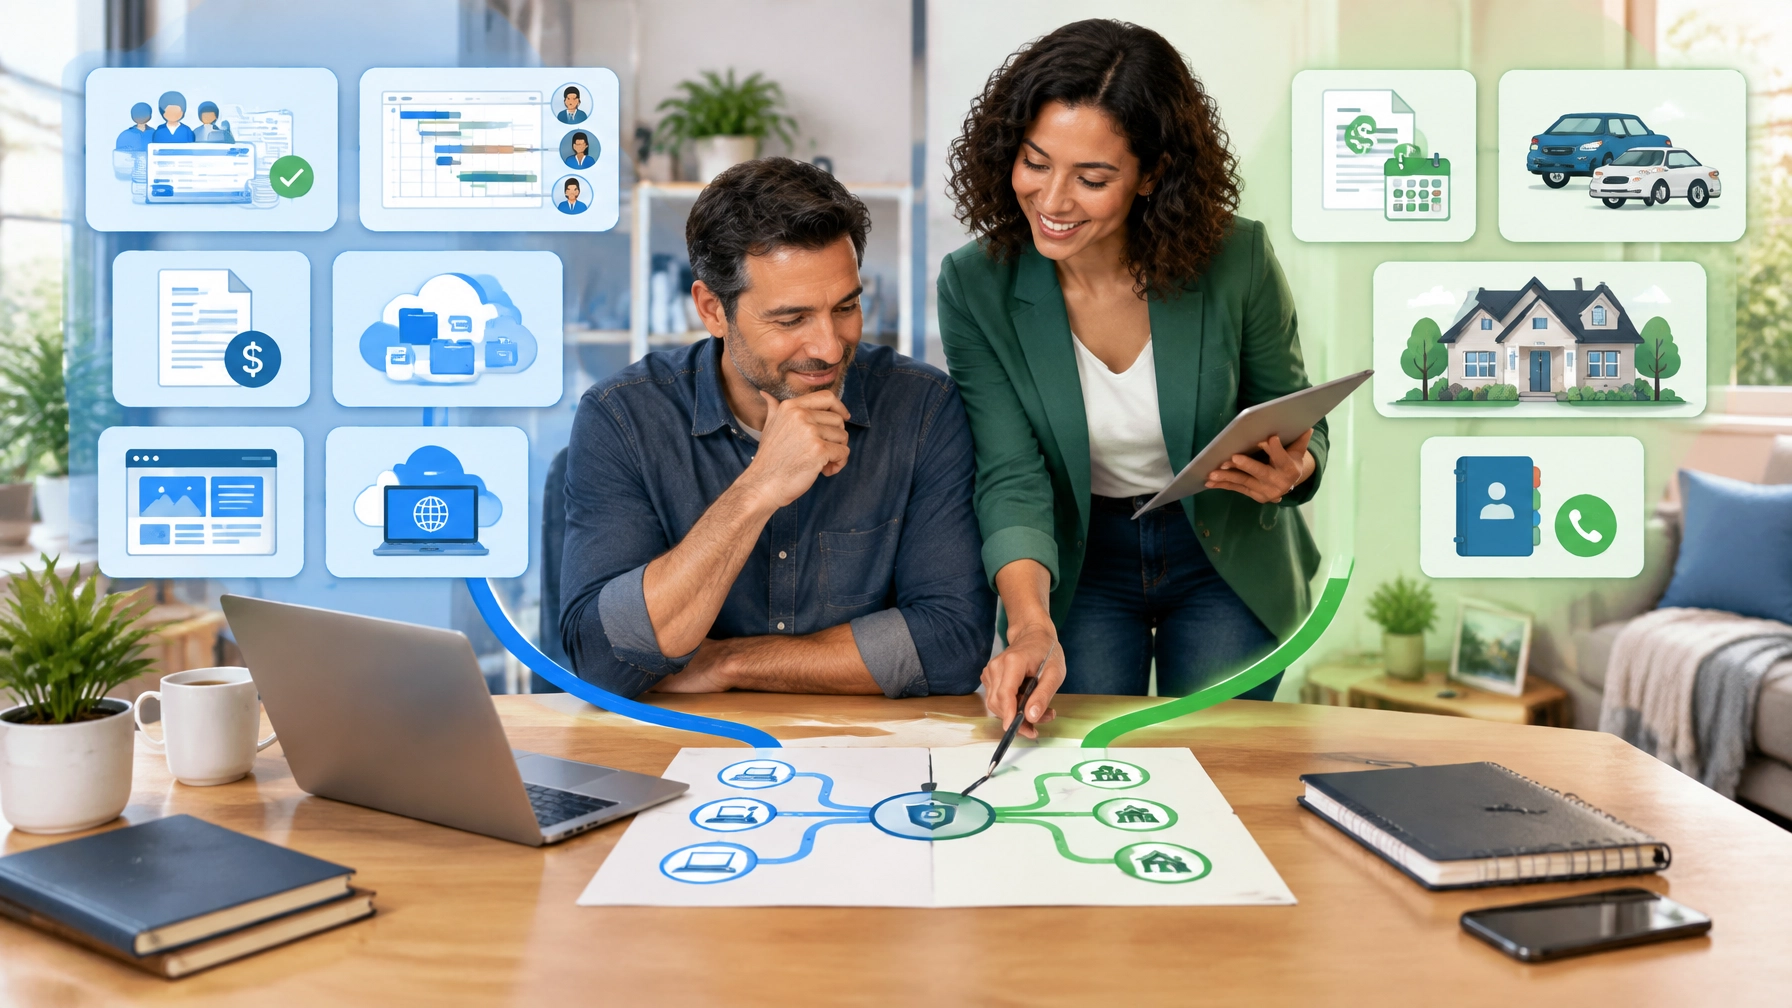
Many small businesses now operate in three places at once: the office, the home office, and whatever happens in between. That sounds manageable until you realize each location changes how company data is accessed, shared, and exposed.
If your team is back in the office part of the week but still handling work from home and on the road, your risk model is no longer built around one network. It is built around identity, devices, and process. That means a return-to-office plan without a security update is incomplete.
The Problem With the Old “Office Equals Safe” Mentality
Many businesses still act like the office network is trusted and everything outside it is the exception. That assumption does not hold up anymore. Conference-room displays, guest Wi-Fi, shared printers, home routers, coffee-shop tethering, and unmanaged personal devices all blur the line.
In practical terms, hybrid work creates three failure zones:
- The office zone: shared devices, meeting room tech, printers, and building connectivity you do not fully control
- The home zone: consumer routers, mixed-use devices, and family networks with uneven security hygiene
- The transit zone: public Wi-Fi, lost laptops, and rushed logins from unfamiliar locations
Sometimes the More Secure Choice Is Fewer Locations, Not More
There is also a more uncomfortable point that many leadership teams skip: if a role can be performed effectively from home, forcing people back into the office may increase complexity without delivering a security benefit. From a pure risk-management standpoint, one well-supported work pattern is usually easier to govern than a split model built around partial office attendance, partial remote work, and constant context switching.
That does not mean every company should be fully remote. It does mean return-to-office should not be treated as automatically safer or more professional. In many environments, it simply creates more locations to secure, more device movement, more exceptions, and more opportunities for policy drift.
Resentment and Low Trust Can Become Security Problems Too
Security is not only about firewalls and MFA. It is also about whether people still care enough to follow the process. When employees feel a policy is arbitrary, punitive, or disconnected from how their work actually gets done, loyalty and buy-in usually drop with it. That matters because disengaged users are more likely to work around controls, ignore guidance, or quietly stop caring about the details that keep a business safer.
In other words, a company can create avoidable risk simply by designing a workplace model that people resent and then acting surprised when security hygiene gets worse instead of better.
Five Security Rules for a Hybrid Team
1. Stop treating location as trust
Whether someone is at headquarters or at their kitchen table, access decisions should be based on identity, device health, and the sensitivity of the resource being opened. Being “inside the office” is not enough by itself.
2. Make MFA and SSO standard
Hybrid work creates more login moments, not fewer. That is exactly why strong authentication and consistent sign-in controls matter. If users are bouncing across apps and locations, you want fewer weak credentials and fewer ad hoc exceptions.
3. Secure the device, not just the building
Endpoint protection, patching, disk encryption, and remote management belong on every business device. If a laptop spends half its life outside your office, the protection needs to travel with it.
4. Separate work from personal convenience
Personal email, personal file-sharing, and random browser extensions are exactly how hybrid work turns into shadow IT. If the company expects flexibility, it also needs approved tools that are actually usable.
5. Write down the policy people are already guessing at
Most hybrid teams are operating on assumptions. Can staff print confidential files at home? Can they use a personal desktop? Are they allowed to save documents locally while traveling? If the policy only exists in your head, it does not exist.
What a Small-Business Hybrid Security Policy Should Cover
- Which devices are approved for work
- Minimum requirements for encryption, updates, and screen lock
- How staff should connect when away from the office
- What data can and cannot be stored locally
- What to do if a device is lost, stolen, or left somewhere
- How access is reviewed when roles change
This does not need to be a 40-page binder. It needs to be clear, enforceable, and connected to the tools your team actually uses.
The Bottom Line
Hybrid work is not just an operations decision. It is a security design decision. If the business has changed where work happens, then IT needs to change how trust is enforced.
At USTech.Ninja, we help small businesses build practical controls around identity, device management, and day-to-day workflow so flexibility does not quietly become risk. If your team is working in more than one place, your policy should reflect that.
Need help tightening hybrid work security? Let’s make sure your return-to-office plan is backed by a real operating policy.